Learning path
Become the CPA everyone trusts with IT controls, SOC and tech risk.
A practical, CPA-led IT auditing path built for SOX, SOC and internal audit work — not for IT engineers.
Most courses included. The following courses on this learning path require the Premium planOffensive and Defensive Security4.5 CPESOC 2 Assessment Capstone5.5 CPESee the Premium plan
Modern audits don’t fail because of debits and credits. They fail because of systems, access and controls. Today’s auditors are expected to do all of this:
ITGCs sit underneath every application control you rely on. If they fail, the rest is unreliable too.
They land in the file whether or not anyone on the engagement can tell you what they don’t cover.
The controls you depend on now live inside someone else’s environment, under a shared responsibility model.
Access, change and availability shape the financial statements as directly as any estimate.
Most CPAs were never formally trained in any of it. This path fixes that — without turning you into an IT specialist.
Nine courses in three stages. Each course assumes the one before it, and the last one puts the whole path to work on a single SOC 2 engagement.
What IT risk is, what an IT audit is for, and what the systems underneath it actually are.
 1
The essentials of IT risk management, controls and governance frameworks, for professionals who need to understand today’s digital risks and compliance requirements.
 2
The types of IT audit, the audit lifecycle, and how to write clear, actionable audit reports — with real-world case studies connecting the theory to practice.
 3
Servers, networks and cloud service models, introduced from the ground up, with the security, compliance and audit considerations attached to each.
The four areas carrying most of the risk in an IT-dependent audit — and how to test each one.
 4
How to evaluate design and operating effectiveness, spot the red flags that surface first, and document findings — worked through real engagement examples.
 5
Evaluating and testing network security from an auditor’s seat: network architectures, infrastructure as code, vulnerability scanning and penetration testing.
 6
SDLC controls, CI/CD pipelines, code repositories and security testing — how to assess risk and evaluate evidence in a fast-moving development shop.
 7
A deep dive into IAM: how to evaluate access controls, identify risk, and assess provisioning and privileged access across modern systems.
How attacks and defences work, then a full SOC 2 examination worked start to finish.
 8
How organisations actually defend themselves — red teams, blue teams and incident response — with the real tools and attack simulations behind each.
 9Capstone
A complete SOC 2 examination from start to finish: evaluating system controls, testing operating effectiveness, interpreting the Trust Services Criteria and assembling a full report on one case study.
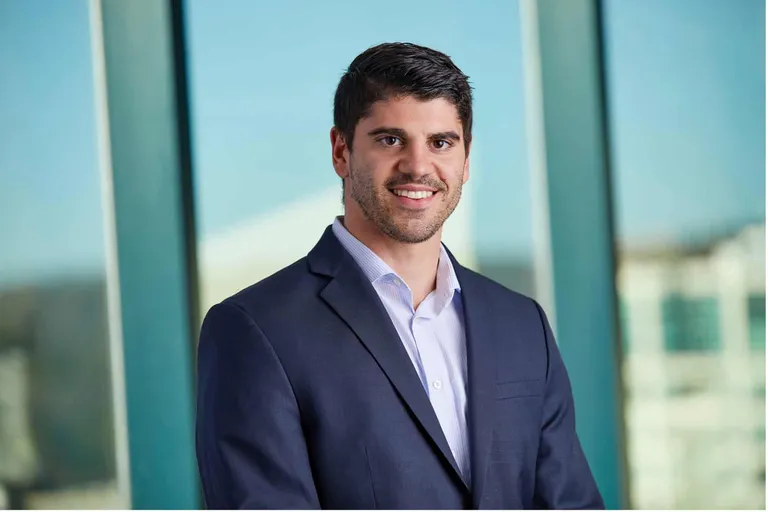
Your instructor
Michael is an accounting and information security professional, and an adjunct professor at several institutions, where he teaches accounting and information technology courses.
He earned his MBA in Accounting and a B.S. in Accounting / Accounting Information Systems from Canisius University. He is a Certified Public Accountant and a Certified Information Systems Security Professional, a current member of the NYCPA’s Education Committee, and an Advisory Board Member for the Academy of Finance since 2020.
By the end of the path, you will be able to:
Durable skill for CPAs in a technology-driven profession.
The path is built for professionals who are:
If your work touches technology, controls or compliance, this path is built for you.
Self-paced
Start, stop and come back. Your place is kept.
Assessed
Work through the lessons, then pass the final exam to complete the course — the standard a NASBA sponsor has to hold.
Credited
NASBA credit for each course is filed to your record the moment you pass.
Most courses included. The following courses on this learning path require the Premium planOffensive and Defensive Security4.5 CPESOC 2 Assessment Capstone5.5 CPESee the Premium plan
Wisdify is registered with the National Association of State Boards of Accountancy (NASBA) as a sponsor of continuing professional education on the National Registry of CPE Sponsors (Sponsor ID: 142016). State boards of accountancy have final authority on the acceptance of individual courses for CPE credit. Complaints regarding registered sponsors may be submitted to the National Registry of CPE Sponsors through its website: www.nasbaregistry.org.